Cybersecurity Analysts Track Intruders Hiding Inside Networks
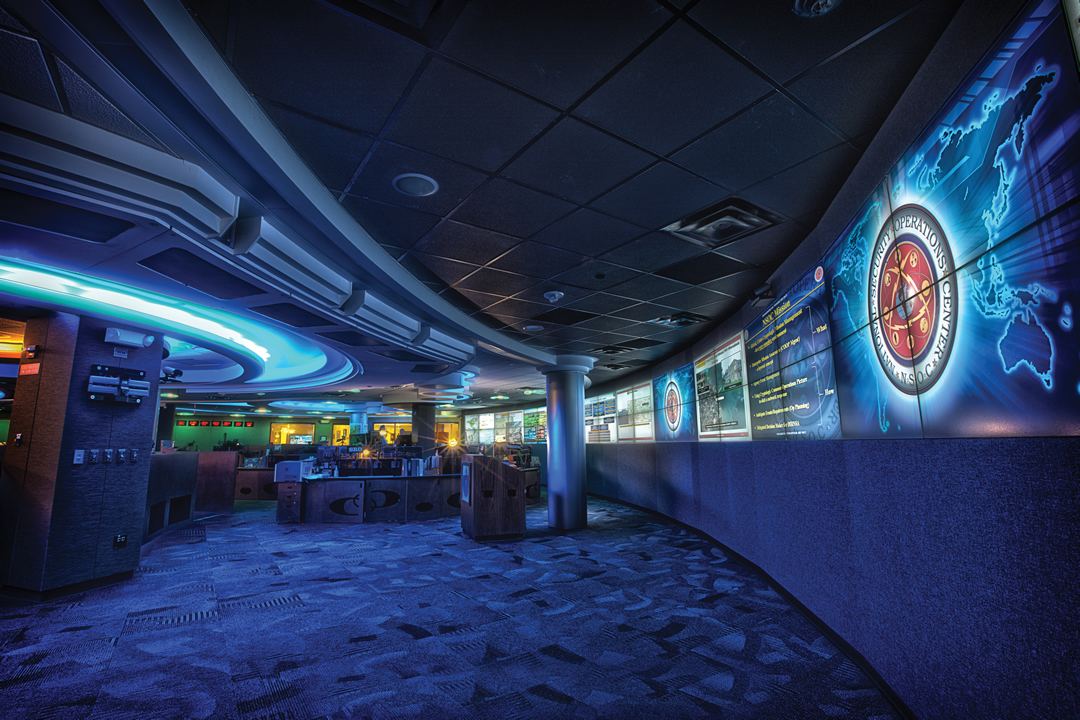
Inside a corporate network, an intruder who has slipped past the outer defences can hide for weeks, moving quietly between computers and gathering access until they are ready to strike. Finding that intruder is the job of cybersecurity analysts, who sift through logs and alerts looking for behaviour that does not belong. The signs are often subtle: a user account logging in at an unusual hour, a server contacting an unfamiliar address, or a file being copied in a pattern no employee would follow. Analysts combine automated tools that flag suspicious activity with their own judgement, built from experience of how real attacks unfold. The work is demanding, because the volume of data is enormous and most alerts turn out to be harmless. Yet catching an intruder early can be the difference between a minor incident and a major breach, which is why large organisations staff their security teams around the clock.
What the Evidence Shows
The tools analysts use are improving, but so are the attackers. Machine learning systems now group related alerts into single incidents and rank them by risk, helping analysts focus on the few cases that matter. Attackers respond by moving more slowly, mimicking normal behaviour and using legitimate tools already installed on the victim’s computers, which makes them harder to spot. Security teams counter with exercises that simulate real attacks, testing whether their monitoring would catch an intruder who behaves like a careful employee. Smaller organisations that cannot afford a full security team increasingly buy monitoring as a service, sharing analysts across many clients. Experts say the human element remains essential, because the hardest part of the job is not collecting data but understanding context, such as whether a late-night login belongs to a travelling executive or a stolen password. In that judgement, they argue, trained people are still ahead of any machine. Reporting and analysis from sources such as MIT Technology Review track the same developments, and specialists following the hidden network intruders say the direction is now consistent across independent lines of evidence.
The Wider Context
The wider context is an industry learning to ship capability and restraint together. Products built around the hidden network intruders now launch with safety evaluations, usage data and rollback plans as standard, because enterprise buyers and regulators ask for them in the first meeting. Companies that treated those questions as friction are discovering they have become the purchase criteria.
What Happens Next
What happens next for the hidden network intruders depends less on another breakthrough than on the unglamorous work of reliability, pricing and support. The buyers evaluating it now are not enthusiasts; they are operators with budgets and auditors, and their checklists will decide the timeline. On the evidence of the current pilots, the technology has earned the right to be judged by them. You can follow related developments in our coverage of technology.
There is a practical lesson in all of this for readers deciding what to do today. Start with the verified facts, be wary of anyone promising certainty, and prefer reversible steps while the evidence is still developing. Circumstances differ by country, income and personal situation, so general guidance should always be weighed against your own context before you act on it in any significant or lasting way.